Cyber Attacks
How Tailgating Works and Simple Ways to Stop It
Physical access bypasses every digital lock you own, making a momentary lapse in door etiquette a permanent breach of your organization's security posture.
Physical access bypasses every digital lock you own, making a momentary lapse in door etiquette a permanent breach of your organization's security posture.
Malware removal fails not because scanners miss files, but because the operating system actively restores deleted components through hidden persistence hooks.
AI red teaming exposes hidden failure modes by simulating malicious user behavior, revealing risks that standard testing and safety filters consistently miss.
Most data exfiltration leaves no trace in security alerts because it travels over authorized channels, requiring you to analyze volume and timing rather than just content.
Most agent failures stem not from model hallucinations, but from unvalidated data flows between the reasoning engine and external tools.
Attackers bypass modern authentication by reading plaintext secrets directly from the memory of the Windows security process, a method that renders many traditional password policies ineffective.
Keeping data longer than necessary increases the attack surface without adding business value, while strict deletion reduces liability but creates operational friction.
Most detection tools fail because they look for artifacts rather than analyzing the underlying signal consistency and physical plausibility of the content.
AS-REP roasting leaves subtle traces in authentication logs that reveal whether an account lacks pre-authentication requirements.
Most response plans fail not because of bad tools, but because they assume human rationality during the physiological stress of a breach.
Device theft reveals itself through silent authentication failures and impossible geolocation jumps before any data exfiltration occurs.
Treating all data as equally sensitive creates blind spots that allow attackers to bypass perimeter defenses and extract high-value records unnoticed.
Cyber threat intelligence transforms raw data into context, allowing defenders to predict attacker moves rather than just reacting to alarms after damage occurs.
Threat intelligence fails when teams collect raw data instead of analyzing attacker behavior, turning expensive tools into storage bins for useless noise.
Extended detection and response correlates siloed telemetry to find attacks that bypass single-layer security controls, revealing hidden lateral movement across your infrastructure.
Attackers bypass password checks entirely by stealing encrypted authentication tokens, rendering standard credential rotation ineffective against active session hijacking.
Most ransomware decryption tools only work because the criminals made a mistake in their encryption logic, not because law enforcement cracked the code.
Persistence relies on the operating system’s startup routines, turning legitimate system features into reliable backdoors that survive reboots and user logoffs.
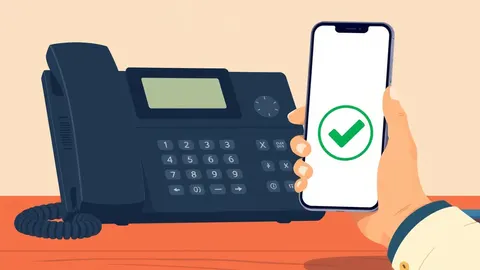
Callback verification breaks the trust chain by forcing callers to prove identity through a separate, verified communication channel rather than accepting their word.
Well-structured disclosure policies prevent legal retaliation and turn independent researchers into a coordinated extension of your security engineering team.
Standard sanitization fails against adversarial examples because they exploit model mathematics, not data hygiene, requiring mathematical defenses.
The EU AI Act classifies systems by risk level, forcing developers to prove safety before deployment rather than waiting for harm to occur.
Most patch failures stem from overlooked dependencies, not missing software updates, creating hidden gaps that attackers exploit.
Scanning a code bypasses traditional URL inspection because the browser trusts the resulting navigation, hiding the destination until it loads.