User Access Provisioning: How Identity Systems Grant and Restrict Rights
Provisioning does not just add users; it silently binds their identity to specific resource policies, creating a hidden chain of trust that persists until explicitly severed.

Provisioning does not just add users; it silently binds their identity to specific resource policies, creating a hidden chain of trust that persists until explicitly severed.

Most malware leaves no files on the disk, so you must analyze volatile memory to find processes that exist only while the computer is running.

Most organizations lose track of half their data stores, creating blind spots that attackers exploit during unauthorized access incidents.

AI risk management fails when you treat it as a code review process. The real danger lies in data drift and emergent behaviors that static tests miss.

LLMs compress data into weights, meaning they retain knowledge from training but lack real-time awareness or inherent truth verification capabilities.

Attackers often bypass technical controls by manipulating human behavior, making immediate account isolation more effective than technical countermeasures during the initial panic.

Revoking access does not remove data already cached in local devices, requiring a separate wipe protocol to prevent silent exfiltration.

Hallucinations are structural features of probabilistic generation, not software bugs you can patch by updating the model version or increasing training data volume.

Security orchestration automates routine tasks so analysts can focus on complex threats, but poor integration creates blind spots that attackers exploit.

Attackers hide persistence in standard scheduler logs by mimicking system maintenance names and using encrypted task definitions that evade basic string matching.

You need security to keep data out of wrong hands, but you need privacy controls to legally process what you keep. They solve different problems.

Scammers exploit operating system telemetry and remote desktop protocols to create fake urgency, bypassing your natural skepticism without ever touching your keyboard.

YARA uses static pattern matching to identify files, allowing you to detect malicious software even when it is encrypted or packed to hide its true nature.

Guardrails shift trust from the model to the pipeline, preventing output manipulation even when the underlying AI fails or is compromised.

Mobile malware often hides inside legitimate apps, using system permissions you granted to bypass standard security controls and steal data silently.

You do not need to defend against both threats equally. Distinguishing between external input manipulation and internal system override determines your security architecture.

Explainability techniques often reveal how a model guesses rather than why it decides, creating a false sense of safety in production systems.

Most login alerts are useless noise because they trigger after the breach is complete, leaving you with no window to stop the attacker from accessing your data.

Most data poisoning attacks succeed not through volume, but by exploiting the model's trust in the statistical distribution of your training set.

Most email filters ignore the sender address header because it is trivial to forge, leaving your organization vulnerable to sophisticated impersonation attacks.

The attack vector metric determines how much effort an attacker needs, shaping the base score before any exploit code is written.

Static scans miss logic flaws, but continuous simulation reveals exactly where your defenses fail when an attacker chains multiple weak points together.
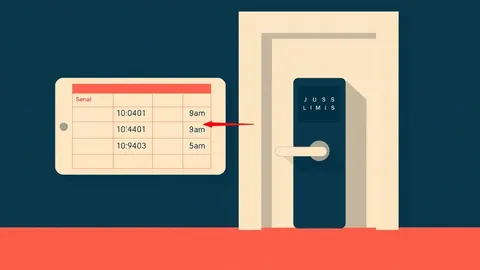
Physical entry logs often reveal tailgating through timestamp anomalies that digital security tools completely miss.

Most script blocking failures stem from allowing scripts in the wrong execution context, not from missing signatures or weak perimeter defenses.